
Govern every file inside your enclave.
Your stack sees every file from the outside. Your catalog indexes its metadata, DLP watches it move, SIEM records who accessed it. None of them read what is inside the file. DataXray does, and federal teams can now acquire it through Carahsoft.
File sprawl is the federal enterprise's largest unclassified attack surface
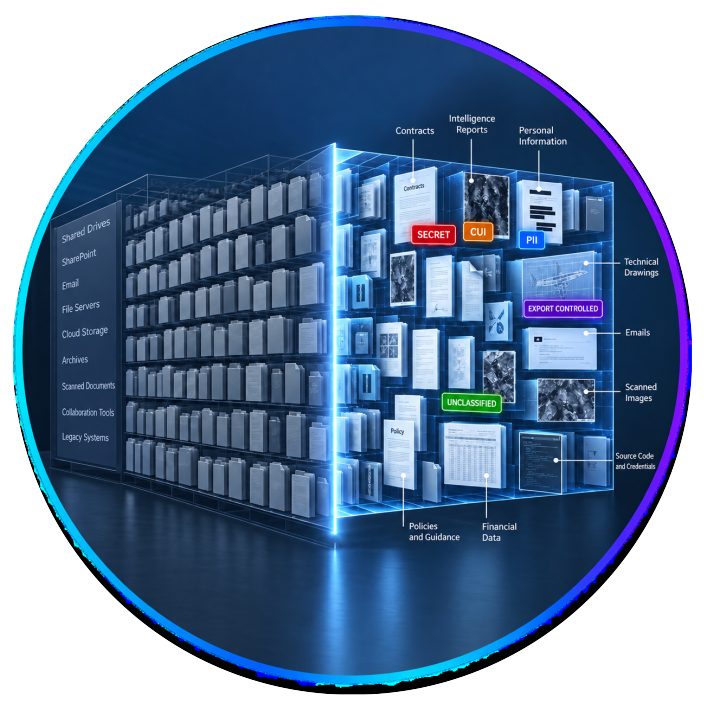
Agencies generate vast volumes of documents, PDFs, emails, contracts, scanned images, and nested archives. These files hold mission-critical intelligence and regulated content, yet the tools meant to govern them never open them. That gap is where AI modernization stalls, compliance findings hide, and exposure compounds. The DoD Zero Trust Strategy calls for classification and enforcement at the file level, at mission scale. Sampling metadata or inspecting the perimeter cannot meet that bar. It takes reading the contents of every file.
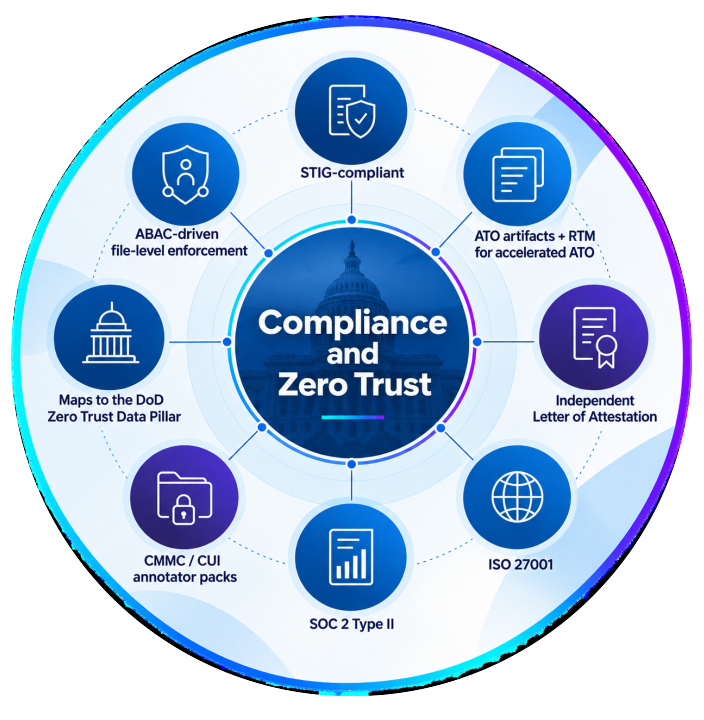
Runs inside your environment. Ready for your auditor.
- You run it yourself, an agentless container on RHEL and Podman.
- DataXray connects with least-privilege service accounts and classifies files where they sit, so nothing crosses your authorization boundary.
- Nothing reaches the outside, so it runs on a disconnected or air-gapped network.
- Users authenticate through your identity provider, so access follows the roles you already manage.
A government-ready way to buy DataXray
Carahsoft, The Trusted Government IT Solutions Provider, makes acquiring DataXray straightforward for federal, defense, and civilian teams. They carry it on established government contracts, so your team can get it under contract and into production with a partner your contracting office already knows.
Bring governance to every file
See DataXray on your own data, and map the fastest path to getting it into your file stores.
You might be interested in…
Here are trending blogs, case studies, press releases and articles from the team at DataXray.
Loading resources...
View all resources